Advanced Exploitation with Metasploit

Minulý týždeň (12-14.11.2010) sme sa zúčastnili bezpečnostného semináru Bez(a)Dis v Košiciach. Osobne si myslim, že náš penetračný tester Norbert Szetei mal jednu z najzaujímavejších prezentácií v ktorej prakticky demonštroval novú funkcionalitu Metasploitu – použitie db_autopwn, vncinject, použitie meterpretera, passiveX ako aj generovanie vlastného trojana.

Videozáznam tejto prednášky, ktorý odporúčam pozrieť je k dispozícií tu.

Samotná prezentácia v PDF formáte k dispozícii tu.

Norbert Szetei pracuje ako penetračný tester pre spoločnosť Nethemba a cieľom prezentácie bolo poukázať na sofistikované techniky, ktoré využívame pri penetračných testoch našich klientov.
more insights

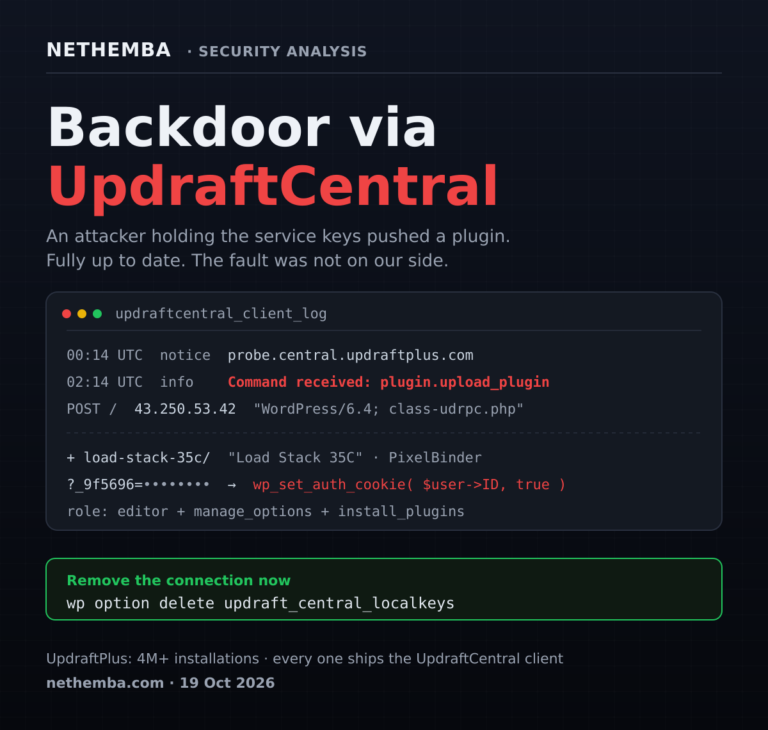
Critical security problem in UpdraftCentral: an attacker holding the service’s keys planted a backdoor on our websites

On the night of 19 October 2026 an attacker abused UpdraftCentral, the remote management service built into UpdraftPlus, a backup plugin with more than 4 million installations, and planted a backdoor on two of our three websites. Our sites were fully up to date and the fault was not on our side: the attacker signed the commands with valid keys that the UpdraftCentral Cloud service generates and keeps. We publish an analysis of the backdoor, indicators of compromise and a way to check your own sites. The vendor later confirmed that the attacker obtained the teamupdraft.com customer database, including UpdraftCentral keys.

Read more >