Blog

Blog

Blog

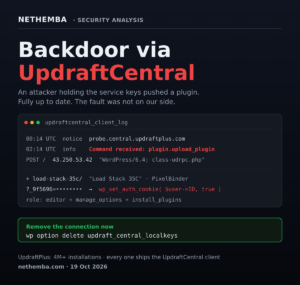
Critical security problem in UpdraftCentral: an attacker holding the service’s keys planted a backdoor on our websites

On the night of 19 October 2026 an attacker abused UpdraftCentral, the remote management service built into UpdraftPlus, a backup plugin with more than 4 million installations, and planted a backdoor on two of our three websites. Our sites were fully up to date and the fault was not on our side: the attacker signed the commands with valid keys that the UpdraftCentral Cloud service generates and keeps. We publish an analysis of the backdoor, indicators of compromise and a...

Read More

Discovery of CVE-2022-24833

When on a security audit for a client it was discovered that a key component – the open-source private paste service PrivateBin contained a previously undocumented flaw. Cross-site-scripting is nothing new. I actually feel there must be prehistoric cave paintings and markings somewhere in the world containing some variation of <script>alert(1)</script>. Although XSS payloads embedded […]

Read More