chroot-restrict sftp only access and full shell ssh login with no chroot restrictions for the same unix account HOWTO

chroot-restrict sftp only access and full shell ssh login with no chroot restrictions for the same unix account HOWTO

A few days ago I’ve tried to figure out, if it’s possible to chroot-restrict sftp only access to some files for particuler user account, while allowing for full shell ssh login with no chroot restrictions from some company internal ip addresses for this same unix account.
It is indeed possible, here is the sample config, where we enable full  shell access for user “user1” from internal trusted IP addresses 10.0.0.1, 192.168.3.6 and 10.0.8.0/24 subnet, while access with this same account from any other IP address is chrooted, disabling TCP and X11 forwarding and login is also permitted with password in addition to private/pubic key authorization.
As usual, for chrooted access to work, /home/user1homedir must be root-owned and have proper permissions.

# extract from main sshd_config file                                          
PasswordAuthentication no                                                     
AllowTcpForwarding yes                                                        
Subsystem sftp internal-sftp                                                   

# restrictions for unix account "user1" from all IP addresses except          
10.0.0.1, 192.168.3.6 and 10.0.8.0/24                                         
Match User user1 Address *,!10.0.0.1,!192.168.3.6,!10.0.8.0/24                
    PasswordAuthentication yes                                                
    AllowTcpForwarding no                                                     
    X11Forwarding no                                                          
    ChrootDirectory /home/user1homedir                                        
    ForceCommand internal-sftp
 

more insights

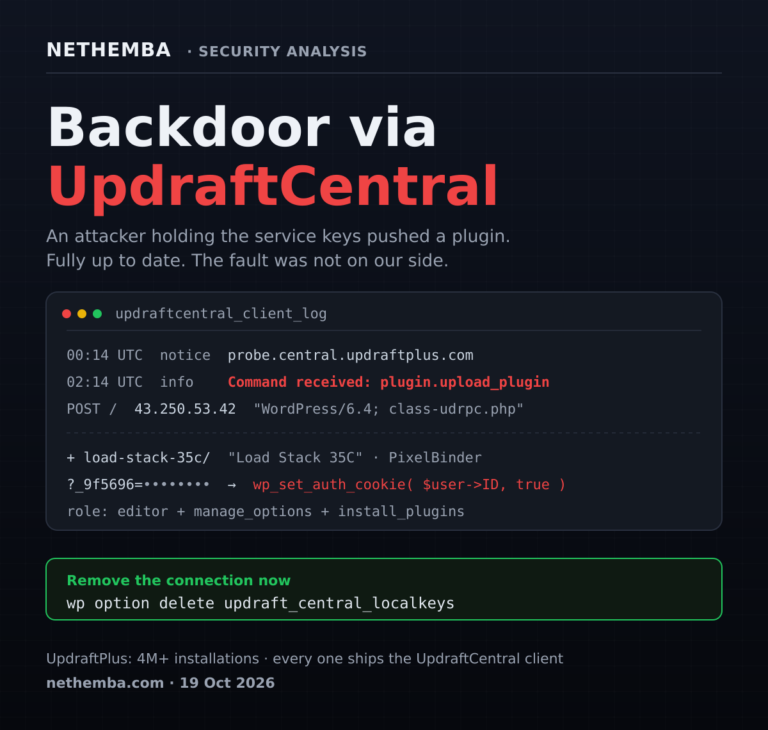
Critical security problem in UpdraftCentral: an attacker holding the service’s keys planted a backdoor on our websites

On the night of 19 October 2026 an attacker abused UpdraftCentral, the remote management service built into UpdraftPlus, a backup plugin with more than 4 million installations, and planted a backdoor on two of our three websites. Our sites were fully up to date and the fault was not on our side: the attacker signed the commands with valid keys that the UpdraftCentral Cloud service generates and keeps. We publish an analysis of the backdoor, indicators of compromise and a way to check your own sites. The vendor later confirmed that the attacker obtained the teamupdraft.com customer database, including UpdraftCentral keys.

Read more >
A broken seal of the commercial register leaking records containing birth numbers

The State as the Biggest Threat to Your Privacy

A senseless Slovak statute published the birth numbers, addresses and certified signatures of company directors — and it is not a bug, it is written into Section 100(3). We are convinced the greatest threat to citizens privacy today is the state itself.

Read more >