Obchádzanie Webových Aplikačných Firewallov

Zajtra (29.3) o 16:30 na MFF-UK v miestnosti F1-108 mám predposlednú prezentáciu o obchádzaní webových aplikačných firewallov (Bypassing Web Application Firewalls). Pri tej príležitosti som sa rozhodol publikovať slajdy k uvedenej prezentácií, samotnú prezentáciu je možné stiahnuť v PDF aj tu.

Dokončil som aj sprievodný “proceeding paper”, ktorý čaká ešte na review Samyho Kamkara.

Je možné, že ide o moju poslednú prezentáciu vytvorenú v OpenOffice Impress, nakoľko ma oslovil nástroj prezi.com.

Posledné 4 bonusové slajdy uvedenej prezentácie nesúvisia nijako s WAF, ale len popisujú najjednoduchší “proof-of-concept” UI redressing útokov ako clickjacking, útok na CSS históriu a potenciálne spôsoby zneužitia.
more insights

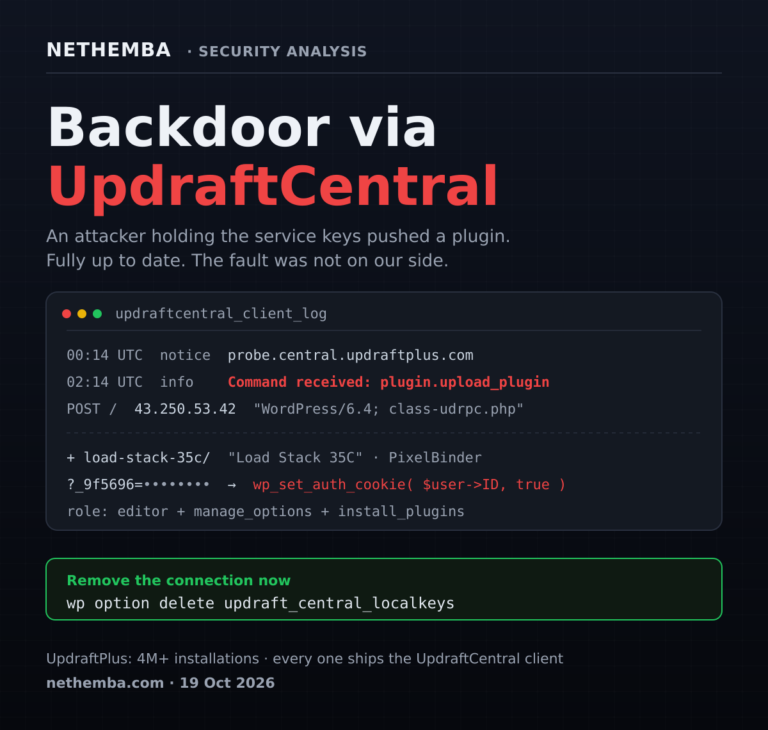
Critical security problem in UpdraftCentral: an attacker holding the service’s keys planted a backdoor on our websites

On the night of 19 October 2026 an attacker abused UpdraftCentral, the remote management service built into UpdraftPlus, a backup plugin with more than 4 million installations, and planted a backdoor on two of our three websites. Our sites were fully up to date and the fault was not on our side: the attacker signed the commands with valid keys that the UpdraftCentral Cloud service generates and keeps. We publish an analysis of the backdoor, indicators of compromise and a way to check your own sites. The vendor later confirmed that the attacker obtained the teamupdraft.com customer database, including UpdraftCentral keys.

Read more >
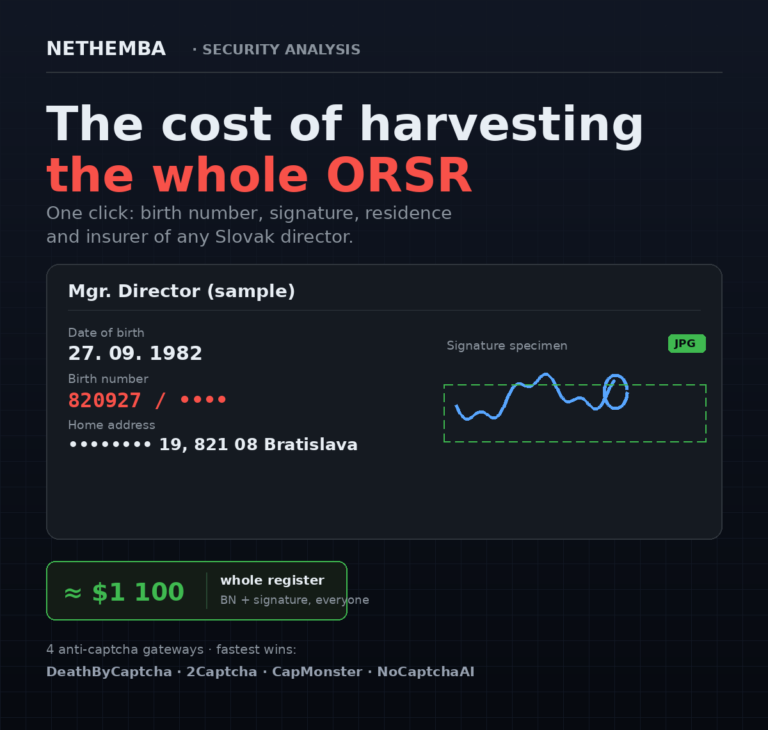
A broken seal of the commercial register leaking records containing birth numbers

The State as the Biggest Threat to Your Privacy

A senseless Slovak statute published the birth numbers, addresses and certified signatures of company directors — and it is not a bug, it is written into Section 100(3). We are convinced the greatest threat to citizens privacy today is the state itself.

Read more >