18.2.2012 mal náš kolega Norbert Szetei zaujímavú prezentáciu o písaní a tvorbe exploitov na konferencii Security Session 2012 v Brne. Okrem klasických “buffer overflow” exploitov sa venoval aj pokročilejším technikám (W^X, ASLR, Canary) ako aj tvorbe ROP exploitov (Return Oriented Programming). Na konci svojej prezentácie interaktívne napísal funkčný exploit ľahko preportovateľný do Metasploitu. Samotná prezentácia k dispozícii tu.
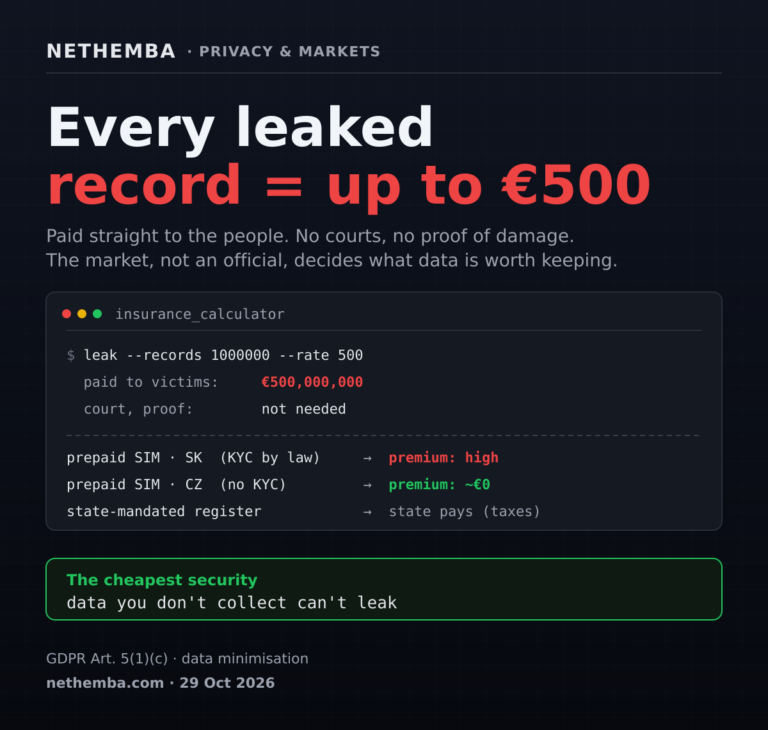
A Market-Based Way to Curb Excessive Mass Data Collection (State Registers, KYC Databases, E-Invoices, etc.)
Governments and companies hoard personal data, and when it leaks, the victims pay the price. A fixed, automatic payout for every leaked record would let the market decide how much data is worth keeping.