New Home Nethemba 2025

We care about
your security.

Nethemba is a leading Slovak IT security firm specialized in web security, penetration testing, and RFID security audits. Since 2007, we’ve been securing businesses with cutting-edge research and expertise, trusted by companies worldwide.

SECURITY

*

SYSTEM

*

ANALYSIS

*

NETWORK

*

DIGITAL

*

SECURITY

*

SYSTEM

*

ANALYSIS

*

NETWORK

*

DIGITAL

About

Nethemba is a Slovak IT security company founded in 2007, primarily focused on web application security and various penetration tests. In addition to the broad portfolio that includes intranet and local system security audits, forensic digital analysis, wireless networks audits and VoIP, Nethemba is the only Slovak/Czech company that offers RFID security audits and active security research which is demonstrated by their regular presentations at worldwide conferences.

Blog

ORSR aggregator (EN)
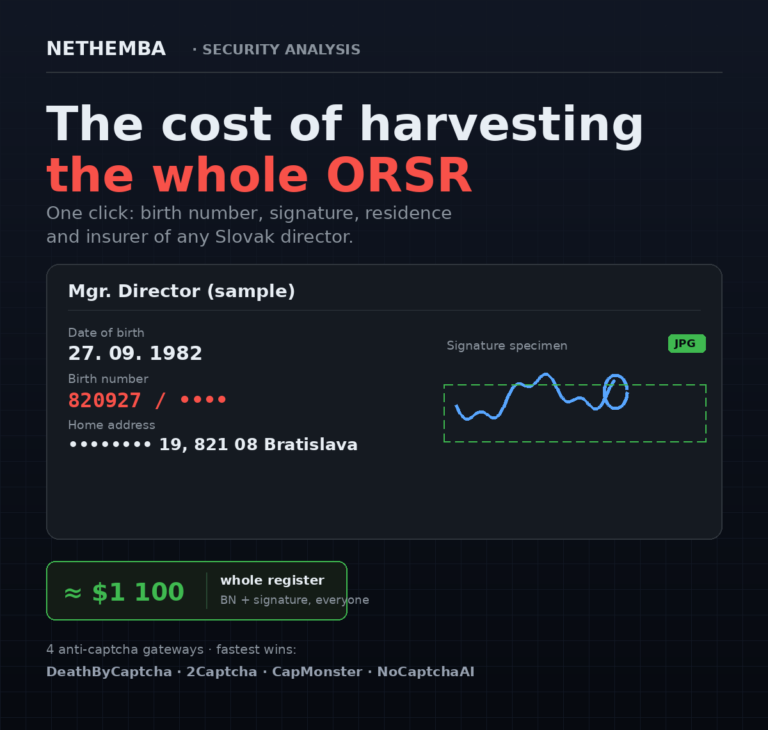
We built an ORSR aggregator and priced out harvesting the whole register (the birth number, signature and health insurer of every Slovak company owner)
In one evening we built an AI-assisted ORSR aggregator: one click gives the birth number, signature,...
ORSR aggregator (EN)
We built an ORSR aggregator and priced out harvesting the whole register (the birth number, signature and health insurer of every Slovak company owner)
In one evening we built an AI-assisted ORSR aggregator: one click gives the birth number, signature,...
A broken seal of the commercial register leaking records containing birth numbers
The State as the Biggest Threat to Your Privacy
A senseless Slovak statute published the birth numbers, addresses and certified signatures of company...

Facebook

Nethemba
Nethemba2 days ago
Agent skill for rigorous bug bounty report triage, validation, severity escalation, and submission-ready reporting.
https://github.com/Sequester-AG/bug-bounty-triage
https://x.com/Zaddyzaddy/status/2108649164615696874
Nethemba
Nethemba3 days ago
How abliterated models can get you pwned
Any open model whose weights have been edited can carry a backdoor, whether it's a task-specific fine-tune, a merged adapter or an abliterated build.
https://projectdiscovery.io/research/how-abliterated-models-can-get-you-pwned
Nethemba
Nethemba5 days ago
During recent discussions about the security of decentralized inference through Routstr, people raised a valid concern: how can we be sure a provider doesn't read our prompts, or alter tool calls to backdoor the machine or the code it generates? Or how do we know the provider does not swap the model for a cheaper one and charge you full price? The usual answer is a TEE, a trusted execution environment. TEEs are hard to audit in practice. You trust the hardware vendor and re-verify a whole software stack after every update. We can do better, and now we do.

Routstr has a confidential mode. Your client talks TLS 1.3 directly to the upstream provider (Venice, for my node), and the Routstr node in between only relays encrypted records. Client and node compute the TLS keys together, so the node can add its API key without ever seeing your prompt or the answer, and it can't change a single byte of the response, tool calls included. Zero-knowledge proofs pin the model and the token cap, and you pay for the usage the provider itself reported. All of this rests on math and on the certificates you already trust, with no enclave or special hardware anywhere.

It works today on routstr.cypherpunk.today, through routstrd (I'm running opencode agents on it) and right in the browser, where the page does every check itself. It's new and experimental, so please try it and tell me what breaks.

Blog: https://juraj.bednar.io/en/blog-en/2026/10/10/confidential-inference-on-routstr-without-trusted-hardware/
Try it in the browser: https://jooray.github.io/routstr-confidential-pwa/
Paper: https://github.com/jooray/routstr-confidential/blob/HEAD/paper/paper.pdf
Code: https://github.com/jooray/routstr-confidential